← goatai.io/glof · Early Warning Architecture
Cryosphere Cascade Early Warning System
A forward vision and reference architecture for multi-sensor, physics-grounded early warning: detecting source failure, tracking corridor propagation, forecasting downstream impact and issuing actionable warning.
For operators of hydropower, water intakes, roads, bridges and border corridors in glacierised or steep mountain terrain.
River gauges remain useful, and they are not sufficient on their own. In a catastrophic cascade the instruments standing in the active corridor can become early casualties of the event they exist to measure. So warning has to begin at the source, continue through the corridor, and keep reasoning when individual sensors disappear.
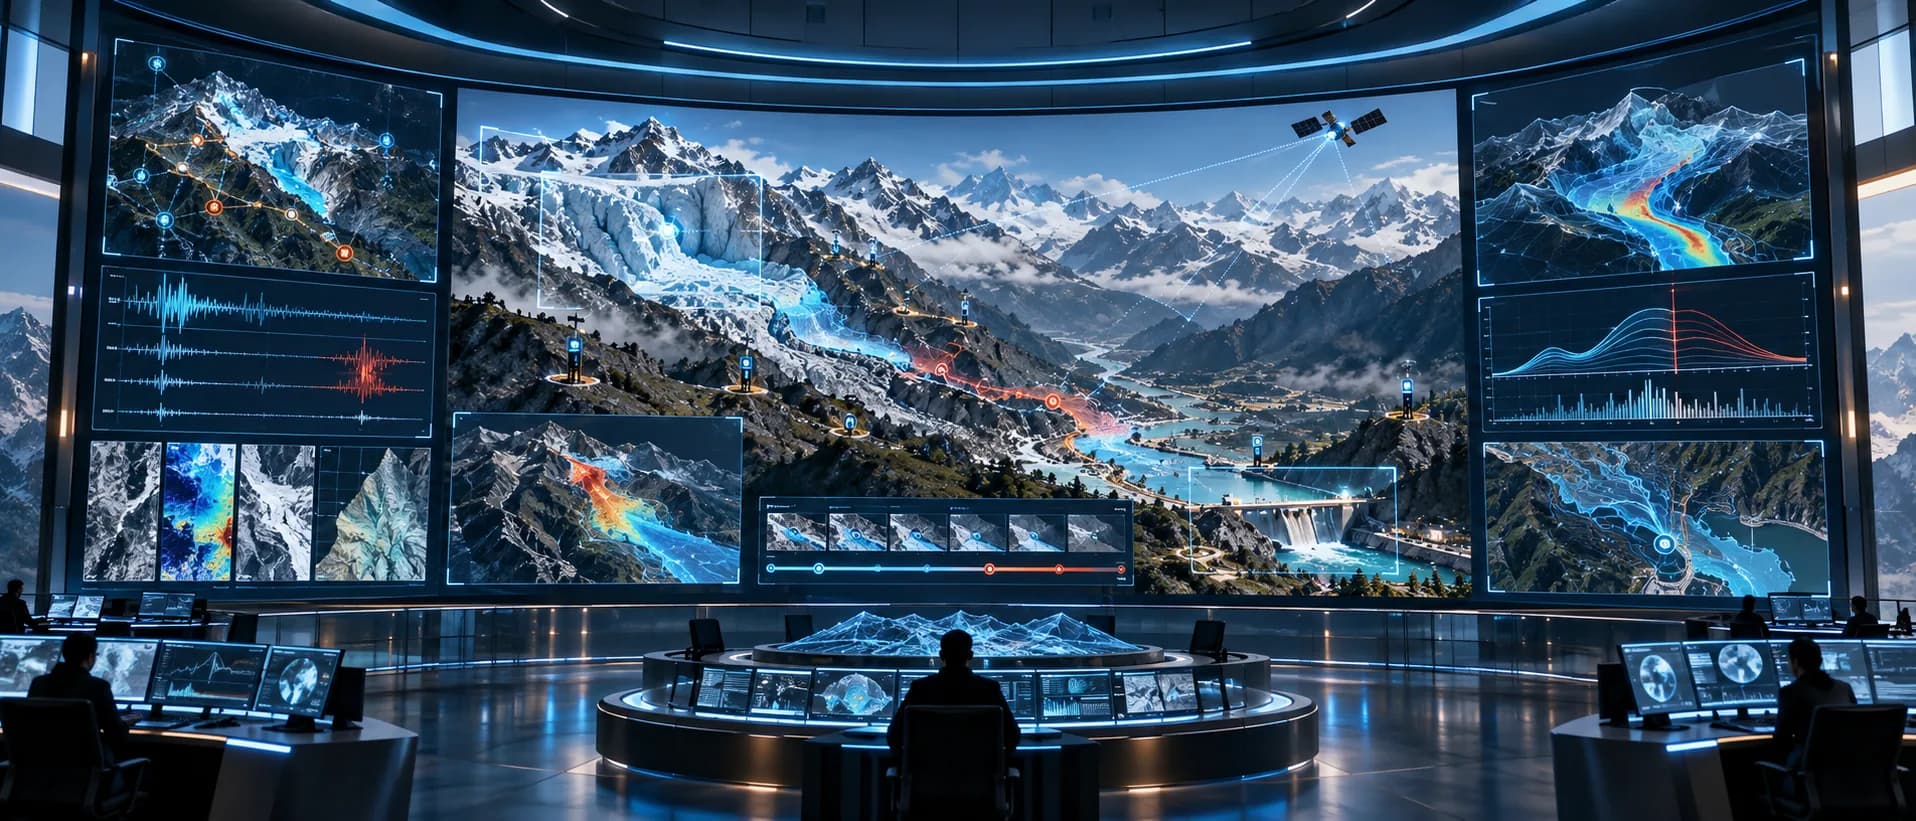
This page presents GOATAI’s reference architecture for a next-generation cryosphere cascade early warning system. It is a design vision — not a reconstruction of a past event, and not a description of a deployed system. The part available today is the corridor assessment it begins with. The control room behind this heading is a concept visualisation, not a facility that exists.
The first step is a sensing-architecture review that starts from the hazard and the instruments already in place — before anything is installed.
01 · Detect
source failure, from the earliest observable signal
02 · Confirm
corridor entry, from independent modalities
03 · Track
front position and velocity along the valley
04 · Forecast
arrival envelope and severity, continuously updated
05 · Warn
asset-specific, with time-to-impact and confidence
Source–channel–corridor architecture · schematic, not a deployment plan
Warnability is set by geometry, before any sensor is chosen
The interval between a credible source failure and arrival at an asset is a property of the distance between them. Where the source sits close above the asset, no architecture recovers time the geometry does not allow. So the first output of an assessment is not a sensor list: it is which of an operator’s assets a warning system can help, which have margin only for automated action, and which cannot be protected by warning at all and need structural or operational measures instead. That classification is available before a single instrument is specified — though it depends on travel time, so on an uncalibrated corridor it is provisional.
Corridor Assessment
What a corridor assessment produces
Before any instrument is specified, a corridor can be assessed using the instruments that already exist and the observational record that already exists. It is the one part of this page available today, and it is useful whether or not anything follows it.
Deliverables
- 01
Corridor hazard architecture — source zones, pathways, exposed assets and expected failure modes.
- 02
Observability inventory — what can already be observed, including instruments the operator may not know are usable — fibre in the valley, seismic stations run by others, archive satellite products.
- 03
Gap register — source-detection gaps, corridor blind zones, exposed sensors, communication gaps and model geometry gaps.
- 04
Per-asset warnability classification — every asset sorted into those where warning is useful, those whose margin permits only automated action, and those no architecture can protect, which need structural or operational measures instead.
- 05
Arrival envelope — calibrated for reaches with a historic event on record; a stated, wider envelope where there is none.
- 06
Prioritised augmentation plan — what to add and in what order, with the reason for each item.
Produced across the first four phases of the deployment arc, taken together rather than one deliverable per phase.
Preconditions
- no site works
- no new hardware or procurement
- no capital approval
- archive data and instruments already in place
It does not place GOATAI in the operator’s warning chain: an assessment issues no warnings and holds no authority.
What it cannot do
It does not deliver warning capability. It establishes what a corridor can observe, which assets warning can help, and what closing the gaps would take.
A corridor with no historic event on record gets a wider arrival envelope with the reason stated, not a confident one from default parameters.
The analysis behind the Nepal 2026 and South Lhonak 2023 reconstructions is the same analysis an assessment applies to an operator’s own corridor.
The Core Problem
What the current generation of early warning cannot represent
Conventional mountain early warning is generally built from thresholds and sirens. It holds no physical-state representation of a propagating event, so it cannot say where the front is, how fast it is moving, or how far to trust what it reports. Gauge fragility is one symptom of that, not the problem itself.
Hazards organised around inventoried lakes
Hazard identification starts from a lake inventory, so a source that is not a lake is not on the map. For a slope failure the first signal is seismic or deformation-related; a stage sensor sees the downstream consequence, not the cause.
Designed for a single pathway
A system built for an outburst flood does not serve a slope failure on the same corridor, though the downstream problem is the same. Where the source sits close above the asset, the interval between failure and arrival can be minutes.
Point sensing on an extended hazard
The hazard runs along a valley; the network observes chosen points. Between stations, tens of kilometres of corridor are unobserved, and a transient blockage can form and release where nothing is instrumented.
Thresholds with no state
A reading crosses a level and an alarm follows. Nothing tracks where the front is, how fast it is moving, or updates the downstream picture as it moves.
Warnings without uncertainty
An operator receives a number with no range, no confidence and no statement of the evidence behind it — and so no basis for weighing a shutdown against a false alarm.
Silent when it can no longer function
Stations in the active channel can be destroyed by the event they exist to measure, and power, communications and mountings fail alongside them. Such systems tend to go quiet rather than declare what they can no longer do.
A river gauge is one observation layer, not the warning system itself. Every design choice below answers one of these six.
System Concept
One intelligent platform, multiple sensing layers
Six domains, each answering a different physical question. None of them is the system on its own, and no site deploys all of them.
Domain A · Wide-area state and precursor context
Spaceborne observation
Optical, multispectral and InSAR: basin condition, lake evolution, slope scars, terrain change, post-event morphology.
Domain B · Failure detection and precursor deformation
Source-zone sensing
Seismic, infrasound, InSAR, GNSS and MEMS observing the slopes that can fail — the earliest observable signal for an abrupt detachment. Seismic and infrasound sensing works at distance, so detection does not require instruments on the hazard itself; deformation sensing does. Where a source zone cannot be reached, powered or maintained, the architecture displaces sensing to accessible ground and accepts the resulting loss in localisation and characterisation.
Domain C · Continuous spatial observation
Distributed corridor sensing
Fibre along the valley: where a disturbance is, whether it is moving, and how fast — between the conventional point stations.
Domain D · Survivable hydrological confirmation
Non-contact river observation
Radar and vision from high ground, outside the active channel, confirming that the river has responded.
Domain E · Stage, weather and local corroboration
Conventional point sensing
Water-level gauges, rainfall and weather stations, structural instrumentation — direct, interpretable, and exposed. The historic gauge record is also the primary instrument for calibrating corridor routing, which is a reason to maintain these stations rather than a concession to them.
Domain F · One evolving physical state
Physics-grounded intelligence
Fusion, state estimation, routing, uncertainty and warning logic. This layer is the product; the sensors are inputs to it.
Multi-sensor stack · every modality resolves into one state representation
Instrumentation
What each modality observes, and where it stops
Twelve sensing modalities, each with its role, its strength and its limit. They do not play the same part: some carry the event as it happens, some establish the geometry and hazard state it runs through, and some supply conditioning context — and they do not share a latency, since a seismic trigger and a satellite revisit belong to different timescales. The platform is modular and site-specific: a deployment uses the subset that closes that corridor's gaps.
| Modality | Function | What it observes | Role in warning | Strength | Limitation |
|---|---|---|---|---|---|
| Satellite optical / multispectral | geometry / state | Glacier extent, snow and ice state, lake evolution, slope scars, terrain change, post-event morphology, basin condition. | Recurrent basin surveillance, change detection, event context, post-event evidence. | Large spatial coverage at low marginal cost. | Revisit interval and cloud cover; usually not sufficient for low-latency trigger detection. |
| InSAR | geometry / state | Slow ground deformation, slope displacement, unstable rock and ice masses, creep zones, long-term precursor motion. | Identify unstable source areas, monitor deformation trends, update the source hazard state. | Distributed deformation measurement over large terrain. | Coherence constraints, revisit interval, line-of-sight sensitivity. Not a solution for abrupt failures. |
| Seismic / geophoneEarliest signal | event sensing | Slope failure, energetic mass movement, debris movement, ground vibration, corridor passage signatures. | Rapid source-event detection and accurate event timing; distinguish major mass movement from background. | Potentially the earliest available trigger signal, and it does not respect the border — a source across a frontier is still recorded. | Reliable event classification and source characterisation require signal processing and corroboration; latency depends on network geometry, signal quality and the detection workflow. |
| Infrasound / acoustic | event sensing | Large energetic surface processes, avalanche and collapse signatures, debris movement. | Complementary source detection, cross-checked against seismic. | Remote detection without corridor access. | Atmospheric and environmental noise. |
| MEMS | event sensing | Acceleration, vibration, tilt, local displacement, structural or slope movement. | Dense local instrumentation: slopes, structures, temporary blockages, local state confirmation. | Low cost and scalable; suits edge deployment. | Point-based with local coverage, and exposed to the hazard if poorly positioned. |
| GNSS | event sensing | Precise displacement, long-term slope motion, large deformation. | Targeted monitoring of critical unstable slopes; reference for other deformation measurements. | Physically interpretable displacement. | Sparse; requires installed stations. |
| LiDAR | geometry / state | High-resolution terrain, channel geometry, slope morphology, cross-sections, topographic change. | Improve model geometry, detect morphological change, monitor selected critical reaches. | High spatial resolution where it matters. | Deployment cost; limited coverage next to satellite. |
| Radar — terrestrial and non-contact riverSurvivable | event sensing | Water-surface range, surface movement, slope displacement, front passage, channel occupancy depending on configuration. | Survivable non-contact observation from high ground: stage monitoring, corridor confirmation, slope monitoring. | Can sit outside the active flood path; all-weather depending on system. | Line-of-sight, installation geometry, local coverage. |
| Cameras / machine vision | event sensing | Visible slope change, channel occupancy, debris front, water surface, structural damage, scene change. | Event confirmation, surface-velocity estimation, human-readable operational context, assisted classification. | Intuitive and information-rich for an operator. | Weather, darkness, fog and occlusion. |
| Water-level gaugesNecessary, not sufficient | event sensing | Stage, hydrograph, local river response. | Downstream confirmation, calibration and historical hydrology, ongoing monitoring where survivable. | Direct hydrological observation. | Point measurement; may be destroyed or stop transmitting, and for a rapid cascade the warning can come too late. |
| Rainfall / weather | conditioning | Precipitation, temperature, snow conditions, atmospheric state. | Conditioning variables, rainfall-trigger discrimination, melt context, forecast support. | Essential environmental context. | Does not directly observe many catastrophic trigger mechanisms. |
| Fibre sensing — DAS, strain, temperatureSpatial continuity | event sensing | Vibration, dynamic strain, slope movement, debris passage signatures, corridor disturbance, and temperature-related hydrological signals where relevant. | Continuous spatial sensing along long valley corridors: detect movement between point stations and track propagation. | Thousands of virtual sensing locations along one cable, potentially on fibre that already exists. | Cable–ground coupling matters, telecom fibre quality varies, traffic and human activity generate noise, and interpretation requires classification. A fibre signature alone does not identify hydraulic state. |
Water gauges remain valuable, but the system must not depend on their survival.
Distributed Sensing
Continuous corridor sensing
Point sensing for point hazards. Linear sensing for propagating corridor hazards.
What distributed fibre adds
A mountain cascade is spatially elongated: it happens along a valley. Conventional networks observe a handful of chosen points; a fibre route can act as a long distributed array, giving potentially thousands of virtual sensing locations on a single cable — often on fibre already installed for telecoms, hydropower or the road corridor.
From that, the platform can infer where along the corridor a disturbance is, how fast it is propagating, whether the signature is moving, and whether it is intensifying or attenuating.
What it does not give you
Fibre does not measure discharge and does not give flood stage. Cable–ground coupling matters, existing telecom fibre varies in quality and route, traffic and human activity generate noise, and every signature needs classification before it means anything.
So the division of labour is explicit: fibre provides spatial continuity; other sensors provide physical interpretation. Localisation, timing, motion and propagation signatures come from the cable; hydraulic meaning comes from radar, vision, gauges and the physics.
Multi-Sensor Fusion
One physical state, not a wall of feeds
The platform does not display each sensor independently. It maintains a common physical-state representation of the source–channel–corridor system, and every field carries its provenance.
Source state
- stable · deforming · failed
- failure time
- estimated source zone
- source-event confidence
Corridor-entry state
- no evidence · suspected · confirmed
- location
- confidence
Propagation state
- leading-front position
- velocity, acceleration or deceleration
- observed passage times
- active corridor length
- confidence interval
Hydraulic state
- stage envelope
- discharge envelope
- debris intensity proxy
- attenuation or amplification
- temporary blockage probability
Sensor-health state
- station alive · degraded · lost
- communication path status
- timing integrity
- data staleness per stream
Asset exposure
- road and bridge exposure
- hydropower asset exposure
- settlement exposure
- coverage lost, by asset
Forecast state
- earliest plausible arrival
- most likely arrival
- latest plausible arrival
- severity band
- uncertainty band
Measured · derived · modelled · inferred
These four categories are never merged, visually or semantically. A measured stage, a derived front velocity, a modelled arrival envelope and an inferred blockage probability are different kinds of claim, and an operator deciding whether to shut down an intake is entitled to know which is which.
Platform Intelligence
What the platform does with all of it
Eight functions between raw observation and an operator decision.
Observation ingestion
Heterogeneous sensors, streaming and batch, satellite updates, edge telemetry, third-party feeds.
Sensor health
Communication status, timing integrity, power state, missing-data detection, confidence weighting.
Event detection
Anomalies, trigger classification, multi-sensor coincidence, false-positive reduction.
Data fusion
Spatial alignment, temporal synchronisation, confidence weighting, evidence reconciliation.
Physical-state representation
Source, channel, propagation, assets, forecast — one representation, not a set of dashboards.
Forecast engine
Physics-based propagation, scenario ensemble, uncertainty propagation.
Warning engine
Thresholds, confidence logic, consequence logic, escalation.
Operator layer
Event timeline, current state, evidence, arrival estimate, map, sensor health, recommended actions — plus what the state alone does not show: which sensors confirm each field, and what changed since the last update.
Common event representation
event ID · origin time · source location · event type and candidates · evidence confidence · active sensors · failed sensors · front location · front velocity · severity envelope · predicted asset impacts · arrival-time envelope · uncertainty · latest update time · recommended response state
One object, versioned as it evolves, so that what the system believed at T+14 is still recoverable after the event — for a board, an insurer or a regulator asking what was known when.
Event Logic
From background surveillance to asset-specific warning
Six states. The system escalates on evidence, and each stage names what it observes and what it does.
Stage 0
Background surveillance
Observes Slope deformation, lake state, weather, glacier condition, river baseline, sensor health.
Action No warning. Maintain state and watch for change.
Stage 1
Source anomaly
Observes Abnormal InSAR deformation, GNSS acceleration, unusual seismic activity, visible slope change.
Action Raise the surveillance state.
Stage 2
Trigger event detected
Observes Large seismic mass-movement signature, rapid slope movement, sudden structural change.
Action Create a candidate event, localise the source, assess corridor coupling.
Stage 3
Corridor entry suspected or confirmed
Observes Fibre propagation signature, radar stage change, camera confirmation, geophone signatures, gauge anomaly.
Action Activate propagation forecasting; issue the first arrival envelope.
Stage 4
Propagation tracked
Observes Successive passage times and front positions from independent modalities.
Action Refine front location, velocity, magnitude, uncertainty and downstream arrival.
Stage 5
Asset-specific warning
Observes Probability, consequence, time-to-impact and redundancy of evidence.
Action Advisory, watch, warning or emergency action — mapped to the operator's own escalation policy and a pre-agreed action set.
Physics-Grounded Forecasting
A live state estimator, not a simulation viewer
Sensing establishes what is happening now. Physics constrains what happens next — and the forecast is re-estimated as each new observation arrives, not run once at event start.
Detect → forecast → observe → update → forecast again
This is not detect the event, run the model once, publish an arrival time. Each new observation updates the estimated physical state and the downstream arrival envelope, so what a control room reads at any moment is the current best estimate rather than a result computed at the start and left standing.
What the forecast engine carries
- corridor routing, calibrated against a historic corridor event and frozen, with source scenarios held as an ensemble
- temporary obstruction scenarios
- propagation timing, attenuation and amplification
- asset interaction along the corridor
- uncertainty envelopes, propagated rather than collapsed
- continuous assimilation of new observations
On an uncalibrated corridor, the arrival envelope is weakly constrained and may appear spuriously precise if default parameters are treated as known. It can still be bounded — through corridor geometry, plausible parameter ranges and ensembles — and is carried wider, with the reason stated. On one reconstructed corridor, observed timing rejected the routing configuration as parameterised, in the direction of overstating the travel time available (Nepal 2026).
Every forecast states four things
A central estimate, an uncertainty range, a confidence level and the evidence it rests on. Arrival is an envelope — earliest plausible, most likely, latest plausible — not a single minute, and severity is a band rather than a number.
Operational warning does not require the mechanism to be resolved. If a source event is confirmed, corridor propagation is detected and downstream impact is projected, warning can proceed while classification stays open. Mechanism certainty is a scientific goal; time-to-impact is the operational one.
That is not a claim that pathways are interchangeable: direct entry, a transient plug and a sustained blockage differ in peak, duration and debris content. What they share is the class of action they demand downstream, which is why the warning path can run ahead of the classification.
Warning-time philosophy
Warning begins at the earliest observable physical state change — days where precursors exist, minutes where failure is abrupt. The objective is to maximise useful warning time for each corridor, not to promise a fixed lead time — within the margin that corridor geometry allows.
Sensor Survivability
Sensor loss can itself be evidence
Instrument health is part of the event state, not a maintenance footnote.
The principle
If three upstream gauges stop transmitting in sequence after a confirmed mass-movement event, the sensor loss can become a physically relevant observation rather than being treated as missing data alone — read in physical and spatial context: correct order, plausible spacing in time, a confirmed source event upstream.
Nepal 2026 is the worked example: three stations stopped transmitting in strict downstream order without recording a rise, and nothing in the chain was built to read that pattern as a detection. See the reconstruction.
And the discipline it needs
Transmission failure may also result from power, communications or equipment faults, so impact should remain a hypothesis until corroborated. A last transmission is an upper bound on the time of loss, no more precise than the polling interval.
Treated properly this is a hypothesis the fusion layer weighs against radar, vision, fibre and seismic evidence. Treated carelessly it is a false alarm generator. What enters the state estimator is four things at once — a communication failure, possible infrastructure loss, possible front passage, and an increase in uncertainty — never a confirmed impact.
Exposure by design · the warning system should not depend on the most exposed instrument
Displacement from the source
Accessibility and detection capability trade against each other. An instrument on the failing slope observes initiation most directly, and is also the least likely to be installed, powered, maintained, or to survive. An instrument on accessible ground several kilometres away observes the same event less precisely and keeps working.
The trade is not uniform across modalities. Seismic and infrasound sensing degrades gracefully with distance: detection persists, while localisation accuracy and source characterisation weaken as the network thins. Deformation sensing does not: GNSS and MEMS measure where they are placed, so a remote installation observes a different slope, not the same slope less well. Satellite observation is unaffected by ground access, but is bounded by revisit interval and cloud.
So the placement question is answered per modality and per corridor, not once for the architecture. Where a source zone is unreachable, the design question becomes how much detection capability is retained at the nearest maintainable ground, and whether that is enough for the warning time the geometry allows.
Walkthrough
Illustrative operating sequence
A hypothetical sequence showing how the proposed architecture could operate during a rapid slope-failure cascade, on relative time from source failure. It includes an instrument loss and an unresolved observation, because a sequence in which every sensor behaves proves nothing.
T+0
detect
Seismic network records a large mass-movement signature. Source state moves from stable to failed; location is an area, not a point.
T+2 min
detect
Source classifier returns a probable glacierised slope failure, with an alternative it cannot yet exclude. The candidate event is created carrying both.
T+7 min
confirm
Distributed fibre shows a high-energy disturbance migrating downstream. Corridor entry moves to suspected: the signature gives location and motion, not hydraulic state.
first envelope issued — wide
T+9 min
confirm
The nearest in-corridor gauge stops transmitting. Treated as a hypothesis, not a gap: consistent with front passage, but power and communications are not excluded, so it raises confidence without confirming anything on its own.
envelope unchanged
T+14 min
confirm
High-ground radar registers a rapid stage change. Independent of the fibre and outside the flood path, so corridor entry moves to confirmed.
envelope narrows
T+18 min
track
A second fibre segment gives an ambiguous return — it may be the front, or a tributary input, or a vehicle on the valley road. Carried as unresolved rather than fitted.
envelope widens
T+24 min
track
Camera confirms a debris-laden front at a known chainage, resolving the ambiguity and giving a measured passage time between two points.
envelope narrows
T+26 min
forecast
Observed propagation is faster than the frozen routing predicted. The forecast is re-estimated on the observation, and the discrepancy is logged against the corridor calibration.
envelope narrows, shifts earlier
T+30 min
warn
Asset-specific warning: time-to-impact, severity band, confidence and the evidence it rests on — issued while the mechanism remains unresolved.
envelope stated with confidence
Conceptual Relative time, no calendar alignment, no corridor. The intervals are plausible rather than measured.
Alerting And Resilience
Escalation on evidence, and a system designed to lose sensors
Alert philosophy
There is no single universal threshold. Escalation combines source confidence, propagation confidence, severity, time-to-impact and consequence:
- source event only → monitor and investigate
- source event plus corridor confirmation → operational watch
- confirmed propagation plus credible asset impact → warning
- short time-to-impact with high consequence → emergency action
Nomenclature and thresholds stay deployment-specific: the platform supports an institution’s own escalation policy rather than imposing one.
Resilience requirements
- no single sensor is mission-critical
- no single communication path is mission-critical
- exposed point sensors are treated as potentially sacrificial
- critical compute and comms sit outside the hazard envelope
- field nodes buffer locally; time synchronisation survives interruption where possible
- sensor quality is assessed continuously, and degraded-mode operation is supported
The system must continue to reason when individual sensors disappear.
Telemetry prefers multiple paths for critical stations — fibre, cellular, satellite, radio, private radio, or a hydropower operator’s own network — without prescribing hardware.
The Last Mile
A warning ends at someone with authority to act, not at a message
Early warning most often fails after the alert is generated. Warning is a socio-technical chain, so this architecture terminates at an interface with a pre-agreed action set — who receives, what they may do, and what they do at each stage.
Who receives, and what authority they hold
Every stage names its recipients and the authority each holds: the engineer who can close an intake, the officer who can stop traffic on a road or bridge, the authority that can order an evacuation. A warning that reaches someone without authority to act is a notification.
Coupled to the operator's existing procedures
Watch, warning and emergency action map onto procedures the operator already runs, not onto a parallel scheme. The system supplies time-to-impact, confidence and the evidence behind them; the operator’s procedure supplies the action.
Agreed before authority, not composed during an event
The action matrix — which stage, which asset, which recipient, which action — is agreed before the system holds authority, and exercised as part of proof testing. An action set written while the front is in the corridor is not a procedure.
Delivery confirmed, not assumed
Each warning expects acknowledgement. Silence escalates to the next recipient on a pre-agreed interval, and who received what, and when, is recorded in the same versioned event object.
Earning Confidence
What an unnecessary shutdown costs, and how a new system earns the right to cause one
The asymmetry, stated plainly
A missed event is catastrophic. An unnecessary shutdown is not free either: lost generation, spilled water, an evacuation that will be obeyed less readily the next time. An operator handed a new warning system has no basis for trusting its balance between those two, and no amount of architectural argument supplies one.
Shadow operation first
The system runs on live data while holding no authority: ingesting observations, maintaining state, and logging every warning it would have issued — issuing none. That makes false-alarm behaviour observable on the operator’s own corridor, against their own conditions, before the system can stop a turbine.
Thresholds are then set from that record and from the operator’s own escalation policy, rather than from defaults carried in from somewhere else.
Between Events
A protective function judged on one event, after years of silence
This system may sit a decade and then be measured on a single hour. The governing design parameter is therefore availability at the moment of demand — and availability that is never tested is not high, it is unknown. Everything below is a per-site design parameter, not a claim about any built system.
Proof testing
Exercising the whole chain without waiting for a real event: signals injected at the sensor layer, a recorded corridor event replayed through the live fusion path, and the outputs compared against what that replay should produce.
A site defines the interval and what counts as a pass — end-to-end latency within the corridor’s own margin, the state transitions reached, the warning generated and delivered to the intended recipient. An untested chain is an assumption.
Continuous self-diagnosis
The sensor-health concept extends from event state to system state: timing integrity, every communication path, data staleness per stream, model and calibration currency.
The output is an availability declaration an operator can read on an ordinary day — what the system can currently do, and for which assets — rather than a green light that means only that nothing has crashed.
Degraded mode, declared
The architecture already requires the system to keep reasoning when sensors disappear. The corollary is the harder half: it must also declare when it can no longer meet its function, and name which assets have lost coverage.
Silent degradation is worse than a system known to be off.
Revalidation triggers
Corridor morphology changes after every significant event, so both the calibration and the hazard architecture have a shelf life. What forces revalidation:
- a corridor event, of any size
- a newly identified source zone
- major channel change, aggradation or avulsion
- instrument replacement, relocation or firmware change
Hazard Archetypes
Different initiating mechanisms, common warning architecture
Pathway-agnosticism is the central claim of this architecture, not a feature of it. Corridor sensing, propagation tracking, sensor-loss logic, exposure and warning apply unchanged whatever initiated the event; what differs is the trigger. The architecture is also not region-specific — cryosphere cascades are not a Himalayan phenomenon, and the reconstructions linked below are Himalayan because that is where this work has been done, not because the design is bounded there.
Archetype A · classical GLOF
A persistent lake breaches and releases an outburst flood that routes downstream. Some lake-origin systems provide observable precursor states — lake growth, moraine deformation, seepage, changing hydrological conditions — but their availability and lead time are event-specific.
Reference reconstruction: South Lhonak, 2023.
Archetype B · ice-rock slope-failure cascade
A slope fails, debris enters the channel, and the flood follows by one of several hydraulic pathways: continuous propagation, a transient plug lasting minutes, or a sustained blockage that later releases. The failure is the start of the event, not a precursor to it.
Reference reconstruction: Nepal 2026.
Archetype C · rainfall / landslide cascade
Intense rainfall drives a landslide or channel blockage, which releases as a flood or debris flow. In monsoon regions this is the most frequent version of the hazard: for many operators, annual exposure is monsoon landslides rather than glacial outbursts.
Downstream, it is the same problem — corridor sensing, propagation tracking, sensor-loss logic, exposure and warning apply unchanged. The difference is at the trigger: conditioning variables are observable, and initiation may not be. Covered downstream, open at the trigger.
Corroboration from a documented event
The assumptions above follow from the physics of the hazard, not from any one event. Nepal 2026 is a documented case that bears on four of them: rapid source failure, uncertainty in the hydraulic pathway, loss of upstream instrumentation, and arrival timing that is only as good as the corridor calibration behind it. That event corroborates the need for this architecture; it does not demonstrate that this architecture would have performed as drawn. The reconstruction carries its own caveats and evidence register; nothing on this page depends on reading it.
Deployment
Assessment first, then only what the assessment justifies
The first question is not what new sensor to install. It is what physical state can already be observed from infrastructure that exists. Phases 1–4 are the corridor assessment, complete and useful on their own; Phases 5–6 follow only if the operator decides to proceed.
Corridor assessment · Phases 1–4
Archive data and existing instruments · no site works, no new hardware
Phase 1
Hazard architecture
Map source zones, pathways, infrastructure and expected failure modes, and classify every asset by warnability — where warning helps, where the margin permits only automated action, and where no architecture can protect it.
Phase 2
Instrument inventory
Existing gauges, telecom and hydropower fibre, seismic stations, satellite products, cameras, weather stations.
Phase 3
Gap analysis
Source-detection gaps, corridor blind zones, exposed sensors, communication gaps, model geometry gaps — and which Phase 1 classifications stay provisional until Phase 4.
Phase 4
Corridor characterisation and calibration
Characterise the corridor: terrain and channel geometry, cross-sections, roughness priors, historical observations, morphology, remote sensing and hydraulic constraints. Calibrate routing only where suitable event data exist — against a historic event on the same reach, then freeze the configuration before forward use, since parameters tuned on the event you then test against demonstrate nothing. Where none exist, carry a wider envelope, bounded by geometry, plausible parameter ranges and ensembles, with the reason stated.
If the operator proceeds · Phases 5–6
Only on an explicit decision taken on the assessment's findings
Phase 5
Targeted augmentation
Install only the sensing needed to close the gaps the assessment found, in its order of priority — not a uniform network.
Phase 6
Platform integration
Fuse legacy and new instruments into the common intelligence layer, in shadow operation first: the system holds no authority until its record on this corridor has been reviewed.
Before adding hardware, the assessment looks for what is already there: telecom dark fibre, hydropower and road-corridor fibre, government seismic stations, including regional networks operated for earthquake monitoring, weather stations, river gauges, CCTV, GNSS, satellite access, existing communications infrastructure, and any existing radar or LiDAR. Most corridors can observe more than their operators realise, and targeted augmentation is cheaper and faster to defend than a new network.
Fleet scale · what is shared, and what is per corridor
Shared across a fleet of corridors
- source detection
- the spaceborne layer
- the fusion platform
- the operator layer
Irreducibly per corridor
- calibration of routing on that reach
- exposure of that corridor’s assets
- gap analysis of its instruments
- warnability of each asset on it
An operator with many corridors does not face many copies of this work: assessment effort and cost do not scale linearly with the number of corridors, because the shared layers are assessed once. A fleet-wide prioritisation is itself an output — not every corridor warrants the same treatment, and some warrant nothing beyond the assessment.
Maturity
What exists, what is designed, and what is still open
A vision page is only trustworthy if it marks its own edges. Maturity applies per capability, not as one label over the whole concept: every element of this architecture sits in one of four bands.
Operating — exists and has produced published work
- event reconstruction with a per-datum evidence register
- corridor screening ensembles and per-member consistency checks
- physics-grounded routing as a screening model, with its limits published
- post-event Earth-observation assessment, including negative results
- lead-time reconstruction from an observed gauge record, stated as a property of location
A corridor assessment is built from these.
Designed — specified here, not built
- the fusion layer and the common physical-state representation
- the warning engine, escalation logic and operator layer
- sensor-loss-as-evidence as an automated input
- proof testing, availability declaration and degraded-mode reporting
- shadow operation on live corridor data
Research — open problems
- low-latency discrimination of landslide-type source signals from earthquakes
- classification of fibre signatures into physically meaningful classes
- inference of temporary blockage formation and release while an event runs
- two-phase debris rheology at corridor scale, rather than a bulking proxy
Detection of mass-movement events from seismic signals is established in instrumented Alpine catchments; what remains open is how far that performance transfers to sparse networks in remote terrain.
Site-dependent — decided by the corridor
- every instrument: what exists, what survives, what can be reached
- whether usable fibre is already in the valley
- whether a historic corridor event exists to calibrate routing against
- communication paths, and which of them survive the hazard
- escalation policy, thresholds and who holds authority to act
Boundaries
What this page does not claim
Stated explicitly, because an architecture page is easy to read as a product announcement.
Relationship To Physics-Grounded AI
The sensing layer is not the product
The product is the chain: edge interpretation, sensor fusion, a physical-state representation, physics-constrained multi-scenario modelling, continuous assimilation and warning intelligence. AI does not replace the physics. It interprets heterogeneous observations, maintains the evolving physical state, evaluates competing physical scenarios against evidence, and continuously updates downstream forecasts and warnings; physics constrains how that state can propagate downstream. Neither half is sufficient — a classifier with no routing model cannot tell you when the wave arrives, and a routing model with no observations cannot tell you that anything has happened.
GOATAI’s value here is not ownership of individual sensors. It is integration, physical-state estimation, forecasting and decision support over whatever instruments a corridor has. The broader position is set out here.
Positioning
A catastrophic mountain flood should not have to reach a gauge before the warning system knows it exists
GOATAI’s EWS vision combines spaceborne observation, distributed corridor sensing, survivable non-contact monitoring and physics-grounded state estimation to detect the cascade, track its evolution and continuously update downstream warning.
Reviewing early warning for a corridor you operate?
A sensing-architecture review starts from the hazard and the instruments already in place.